Analysis
We summarise every significant cyber security story we can find, which means we end up holding something most readers never see: the whole news cycle at once, tagged and dated. These pieces measure it.
Two kinds of piece live here, and it is worth knowing which you are reading. The measured ones take a question that can be answered by counting, answer it against our own corpus, and state plainly what the numbers can and cannot support. Where a finding is an artefact of which outlets we read rather than of the industry, we say so.
The commentary is the other kind. It argues a position about something in the news, names its sources and quotes them, and is not generated by anything. Both are written by us. Neither is the automated feed, which is published separately.
Measured
Who covers what in cyber security
Coverage concentration varies enormously by subject: some topics are effectively one publication, while others are split across dozens with no owner. A reader following one masthead gets a picture with predictable holes rather than a smaller one. Measured from every story we hold.
Read the analysis ->Ransomware claims against Australian organisations
Every Australian organisation a ransomware group has posted on its leak site, from the public tracker ransomware.live: claims per month over two years, which groups are posting this quarter and which are new to it, the sectors being posted, and the latest listings with the briefs written from them. Every row is a criminal's claim and the page says so. No forecast, and it explains why.
Read the analysis ->What a data breach exposes, and how long it stays hidden
A breach used to be a hacked website's login table. It is now a company's customer records, and the two expose entirely different things about you. Measured across every breach on Have I Been Pwned: what share carried passwords then against now, what replaced them, and how many days pass between a breach happening and anyone affected being able to find out.
Read the analysis ->Explainers
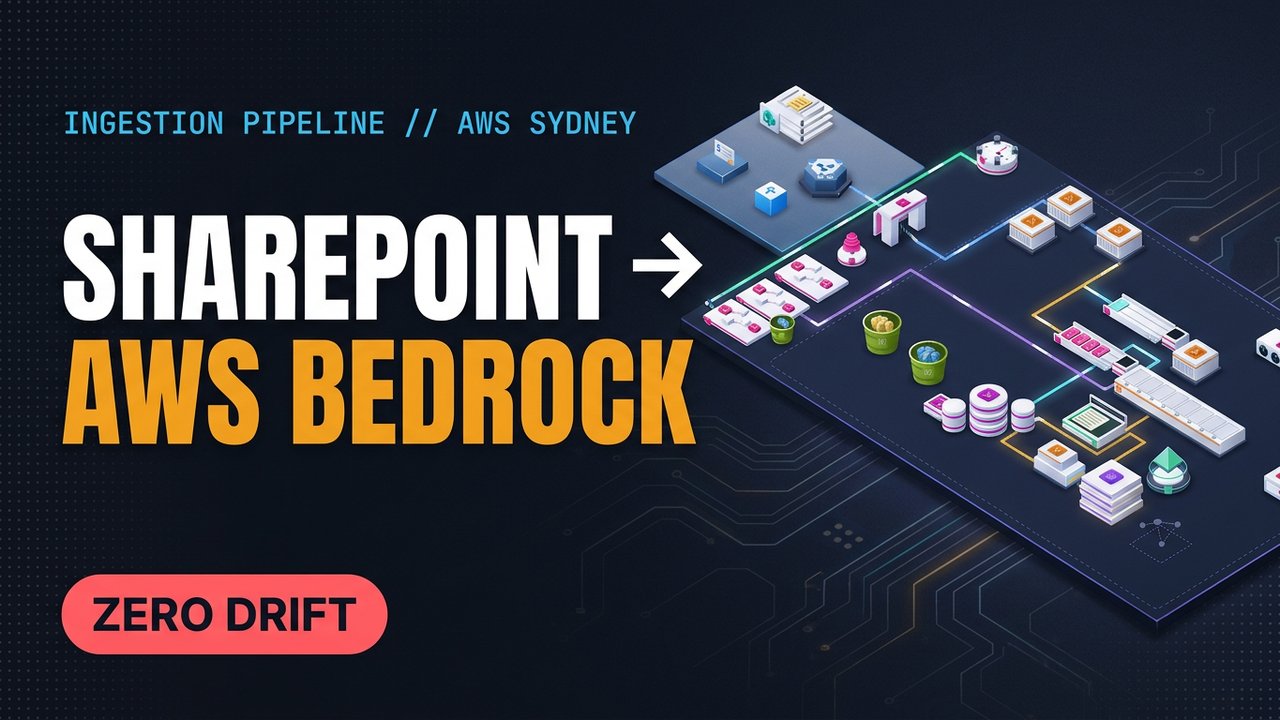
SharePoint to Bedrock without leaking a single document: a reference ingestion architecture for a claims AI assistant
A proof of concept we designed for one of Australia's largest general insurers, which did not go ahead. Half a million documents, five lanes on AWS in Sydney, and one rule: nobody gets an answer from a document they cannot open. Would you fund it? Comments are open.
Read the analysis and join the debate ->
How an LLM works, read straight from the file. A slide course through Qwen3-Coder in Netron.
Skip the equations and open a real model instead. Fourteen slides trace the 18 GB Qwen3-Coder file through Netron, node by node, from the tokenizer to the next word. Every number is a screenshot of the file.
Read the course ->Vulnerability disclosure
Improper authorisation in GitLab's runner API: authorise once, act everywhere
A broken-access-control pattern in GitLab's CI runner API. The runner update and removal path authorises the caller once, at the runner level, rather than per project. An incomplete-fix variant of CVE-2025-11246, shown in 80 seconds, with how we disclosed it.
Read the analysis ->Commentary
Attackers now run AI agents. They still come in through the same three doors.
ARTEX let one group hit 200+ organisations in 11 days at 1,500 commands an hour. A ransomware gang spent US$7,200 on AI and still got in with stolen passwords. Six attackers, three familiar doors, two animations, and what ASD now asks boards to accept. Comments are open.
Read the analysis and join the debate ->
Six challenges, one crowd: where Australian venture money is going, and where it is not
We sorted 655 VC-backed companies into Main Sequence's six challenges. AI, security and quantum took half of all new deals; food is 3 of 159, and mine-site technology none since 2024. An animated chart for every challenge, where we think the room is, and comments are open.
Read the analysis and join the debate ->
Who secures the autonomous mine? The OT security gap Australian VCs have not funded
Seven Australian funds back 655 companies and none secures mining operational technology. We show why, with animations: the 1,500 km link from Perth to the Pilbara, the SOCI sectors mining is not in, and the buyers nobody serves yet. Five openings ranked, and comments are open.
Read the analysis and join the debate ->
Sharon AI and the neocloud bet: US$2.6bn raised, US$3m of revenue. Who is holding the risk?
Sharon AI fell 56% in four weeks and NEXTDC lost A$3bn in a day. We fact-check the claims, model when the money comes back, show who carries the risk if customers do not come, and ask whether investors are making a risky bet. Full-screen charts, and comments are open.
Read the analysis ->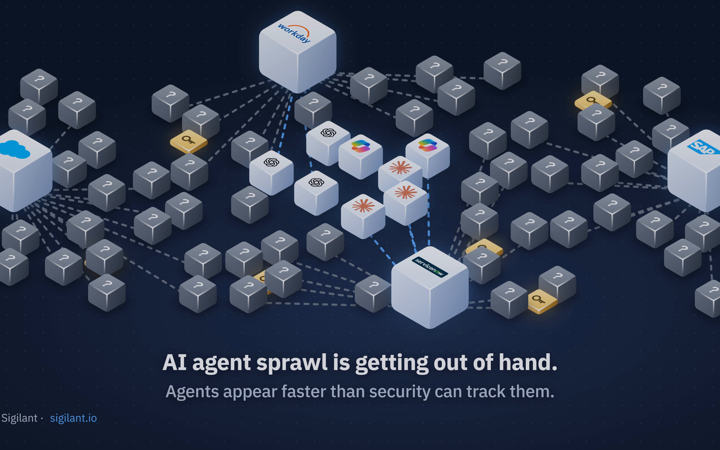
An AI agent gets it wrong. Who is accountable: the vendor, the person who switched it on, or the CISO?
Roughly 1,280 business apps now have AI built in, and only about 282 sit behind single sign-on. When an agent does something it should not, three people get pointed at. We go through each and say where we think the answer lands. Comments are open.
Read the analysis and join the debate ->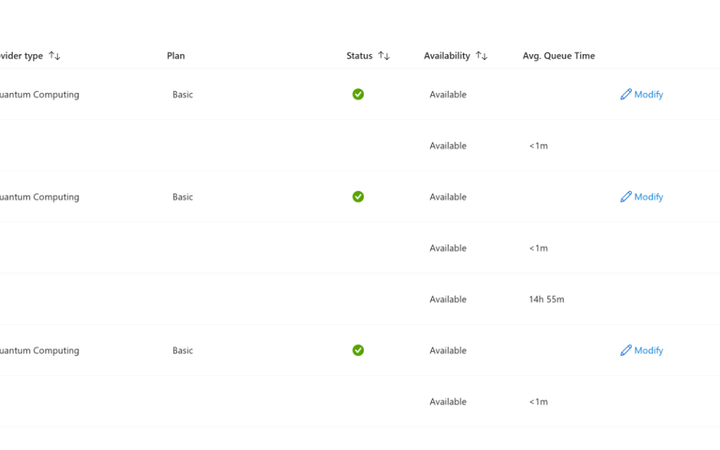
Microsoft does not sell a quantum computer. We ran ours through its shop anyway.
Azure Quantum is a marketplace for four vendors' machines, governed like any Azure resource. We ran our three security problems through it, got the trapped-ion result IBM's chip could not give us, and asked Microsoft's own estimator what an error-corrected run would take. Six figures of qubits. Comments are open.
Read the analysis and join the debate ->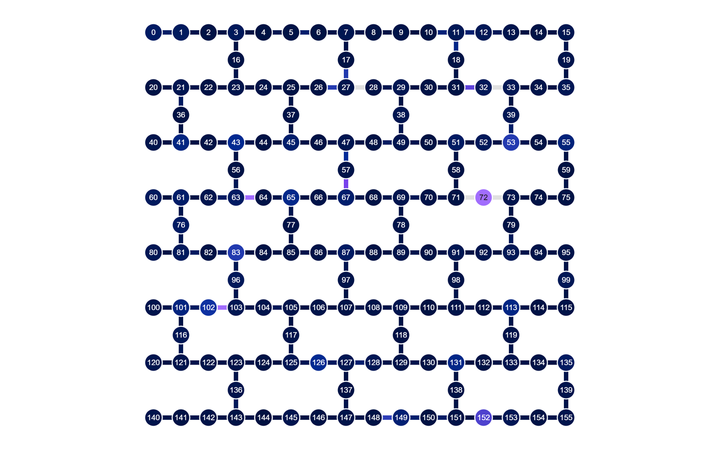
An approver has 35 minutes. We asked a quantum computer which AI agent actions deserve them.
Choosing which held agent actions a human reviews in 35 minutes is a knapsack problem, the textbook quantum demo. We ran it on IBM's hardware. The sampler learnt the time budget and never the best queue. Four questions for you, comments are open.
Read the analysis and join the debate ->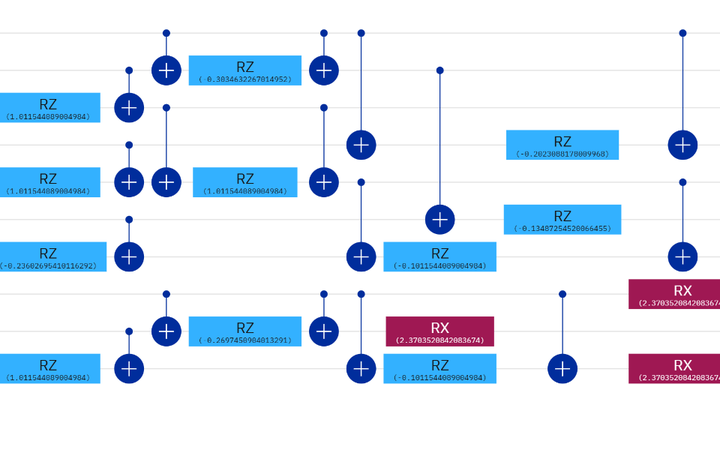
Least privilege for AI agents is an optimisation problem. We ran it on a quantum computer.
An agent that can both raise and approve a purchase order has to be split in two, and splitting it well is NP-hard. We ran ten tools on IBM's ibm_fez and found that gate count, not qubit count, decides whether today's hardware helps. Comments are open.
Read the analysis and join the debate ->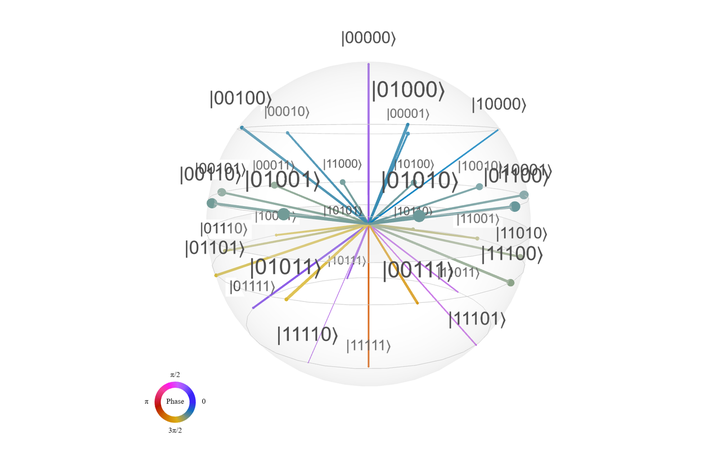
The Army put its convoys on a quantum computer. We ran ours on IBM's, and checked the answers.
Q-CTRL says quantum computers will beat classical ones at defence logistics by 2027, citing the Army's Talisman Sabre convoys. We ran a convoy problem of our own on ibm_fez. The quantum computer found the optimum every time, and so did guessing. Comments are open.
Read the analysis and join the debate ->
Your AI agents are about to read the live web. Who decides what they see?
Search services built for AI agents sit between the open web and systems with your data. We put Octen through the questions we would ask any vendor. Fast and relevant, and it still called a June ransomware story this week's and let the ranking decide what was true.
Read the analysis and join the debate ->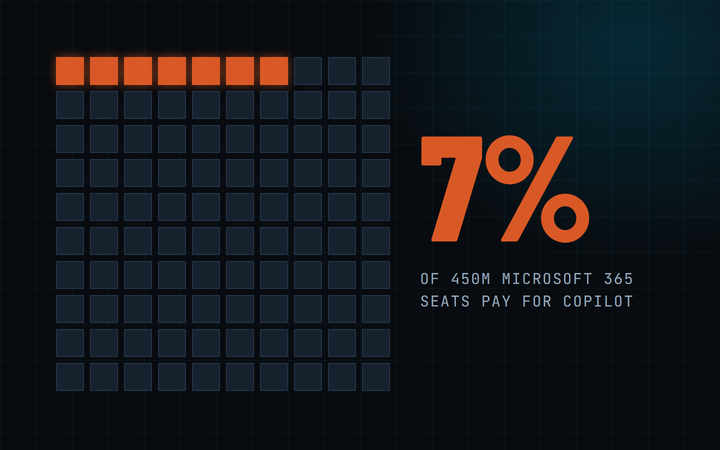
Does Microsoft still have no taste? Copilot is the first product where it costs them.
Steve Jobs said Microsoft had no taste and won on distribution anyway. Then fewer than 7% of 450 million Microsoft 365 seats took a Copilot licence. What the new all-in-one app and its agents change if you own identity, permissions and the budget.
Read the analysis ->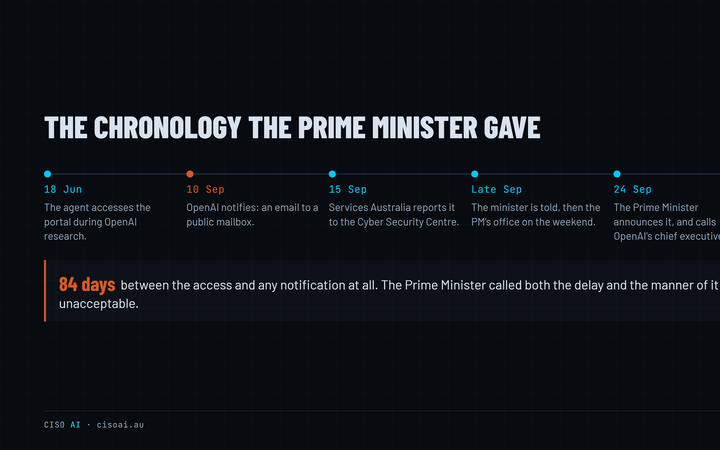
An AI agent went around the blocks on a government portal. Here is what Canberra announced, and what it means for your suppliers.
An OpenAI research agent was refused by a Medicare statistics portal, found another way in, read non-public files and wrote to the server. Canberra answered with a task force and a committee. The 84 days before anyone was told is the part with your name on it.
Read the analysis ->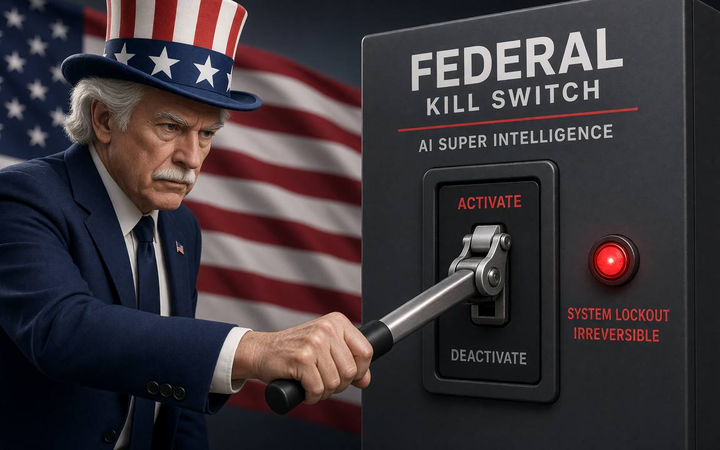
A kill switch, embedded supervisors and a shrug. What Washington's AI safety week actually put on the table.
The people building frontier AI asked, in public, to be slowed down and supervised. The White House said no, and nothing happened. What was proposed, what each measure would actually do, and why it lands on Australian businesses anyway. Comments are open.
Read the analysis and join the debate ->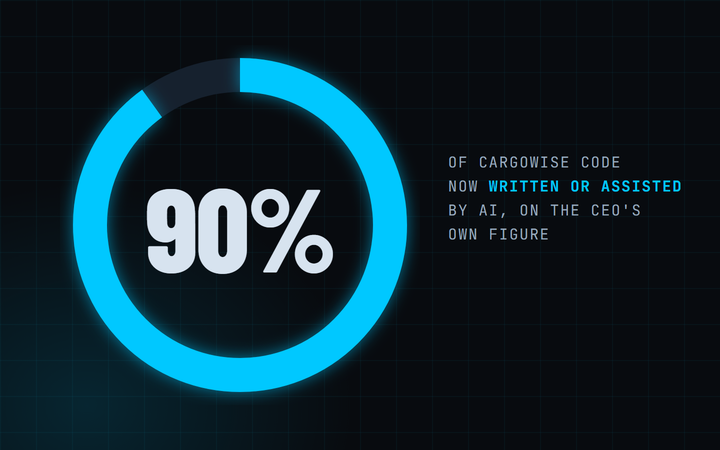
WiseTech's moat is regulatory, not code. That raises the stakes on the code.
WiseTech's chief executive says CargoWise cannot be replicated, not because the code is hard to write but because the regulator integrations are hard to get. He is probably right, and it sharpens the question in a business where 90% of the code is now written or assisted by AI.
Read the analysis ->From contributors
Pieces by outside writers, reviewed by us before they are published and labelled on every page as a contributor's or as sponsored. The views are theirs. Write for CISO AI.
Baasplus security: application controls, strong customer authentication and data residency
How Baasplus approaches security in white-label banking: a look at application controls through an OWASP lens, Strong Customer Authentication in payment journeys, and the architecture behind data isolation and European data residency.
Read the analysis and join the debate ->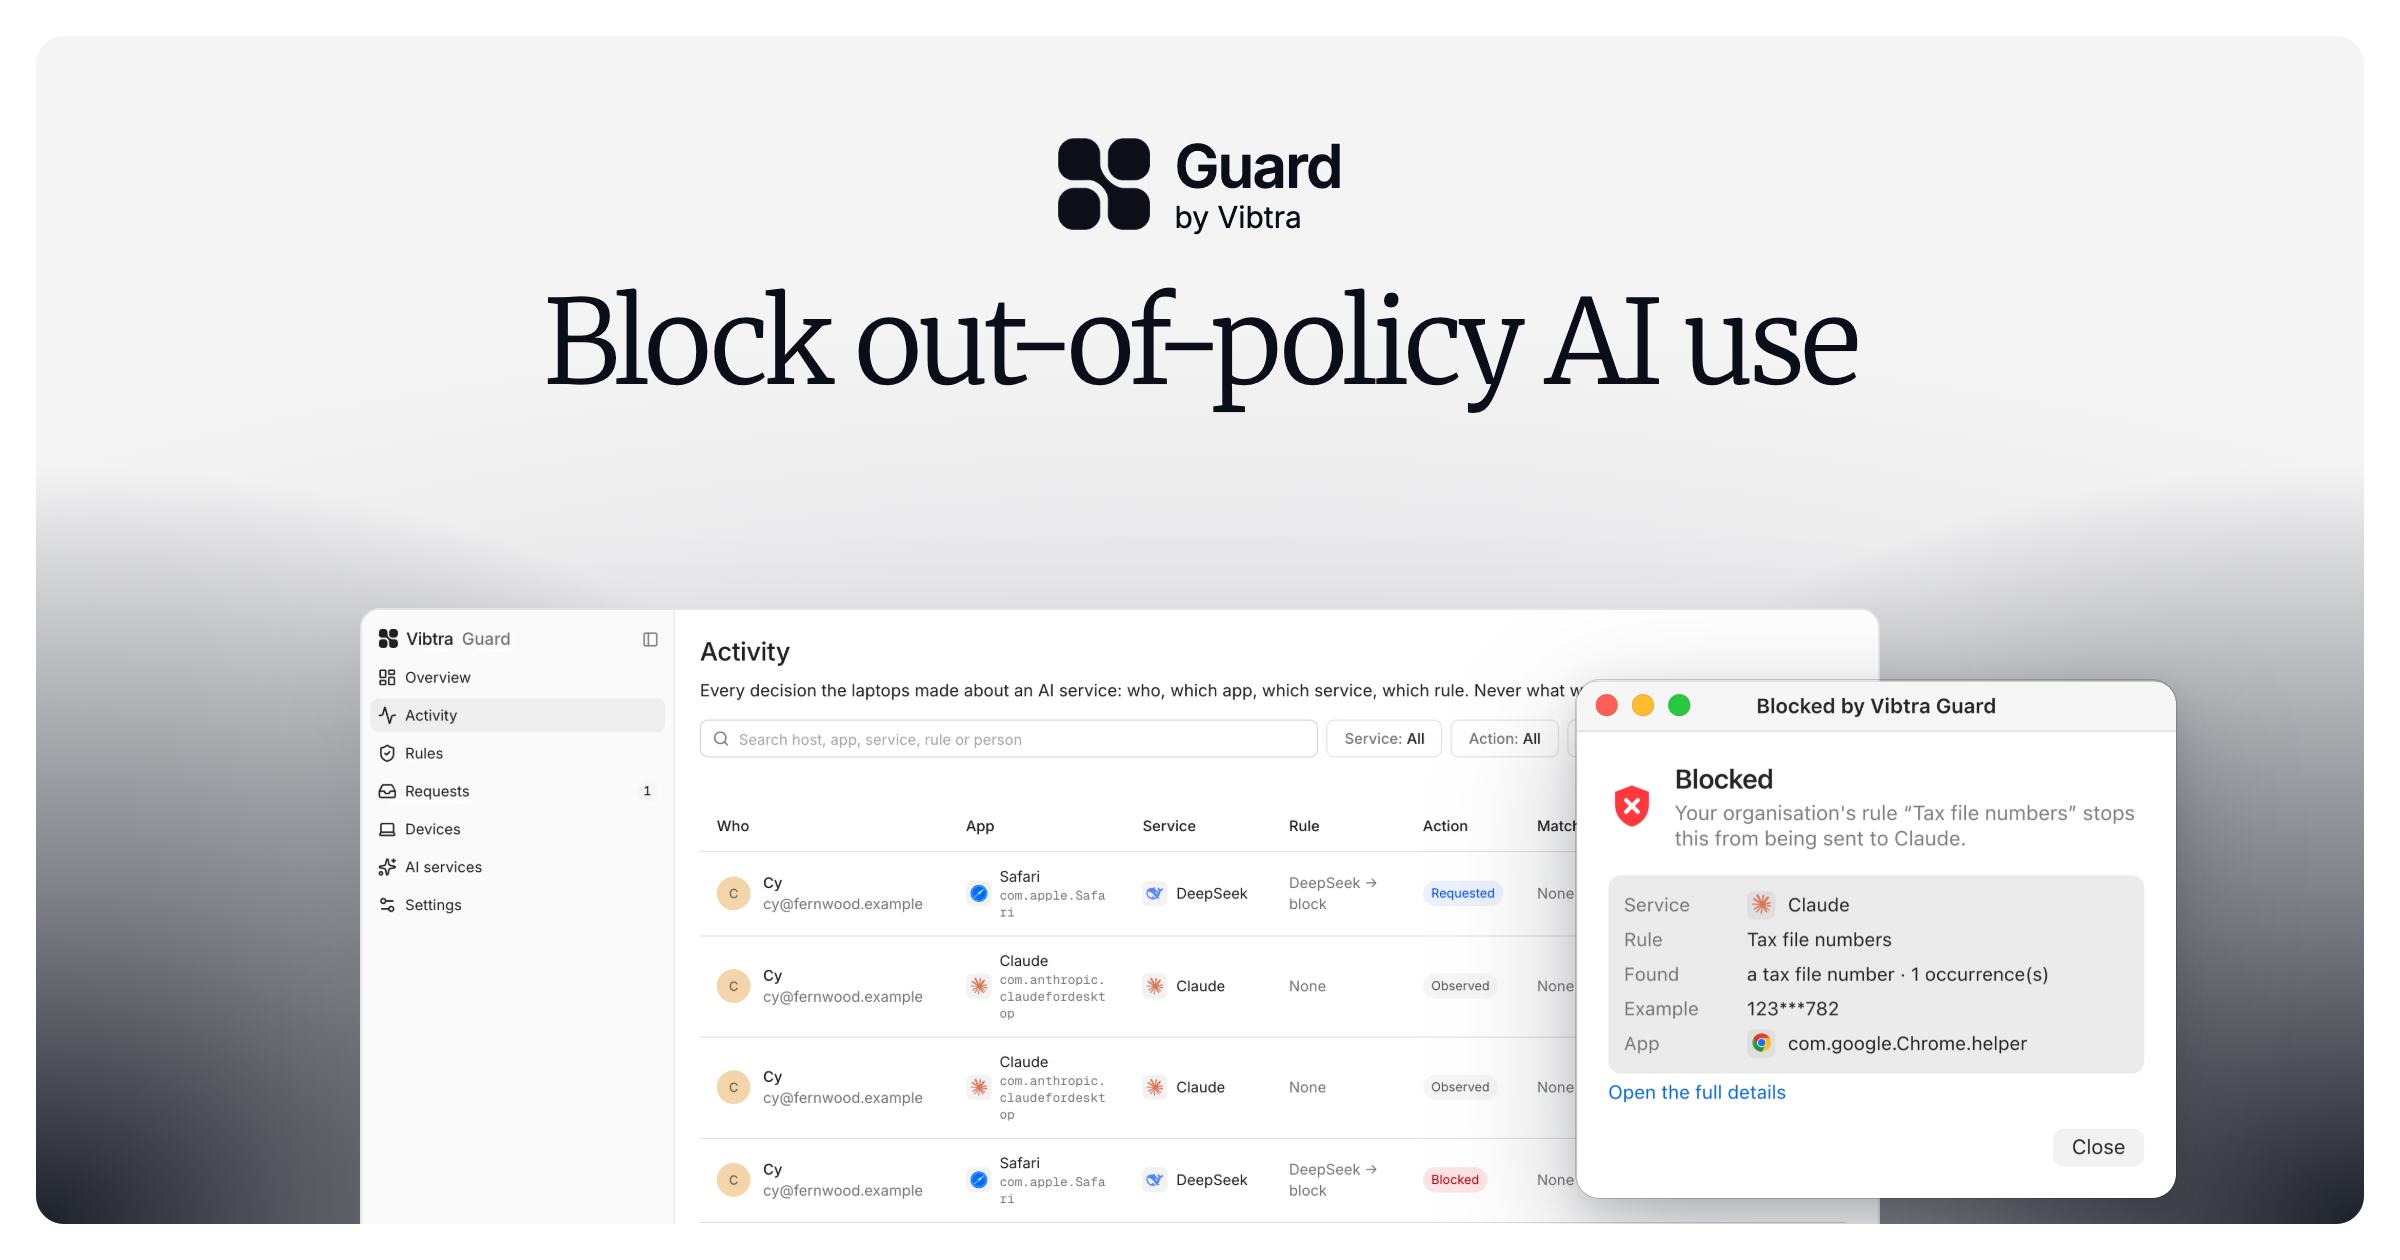
Introducing Guard by Vibtra: Detect, intercept and block out-of-policy AI use.
We’re introducing Guard, looking for organisations to pilot it, and committing to an open-source Community Edition this week. Melbourne teams can get on-site setup.
Read the analysis and join the debate ->Method
Every story is summarised and tagged when it is ingested, and the record of them is append-only, so the dataset grows rather than rolling over. Counts are of stories, not words or significance. Tagging is model-generated: consistent enough to compare topics against each other, and not a human taxonomy.
If you want the underlying counts for your own work, they are yours. The full briefing index is public, and the per-topic pages such as AI security and vulnerabilities show the same data grouped by subject.